- Platform Architecture
Four module groups. One Integrated Control Plane
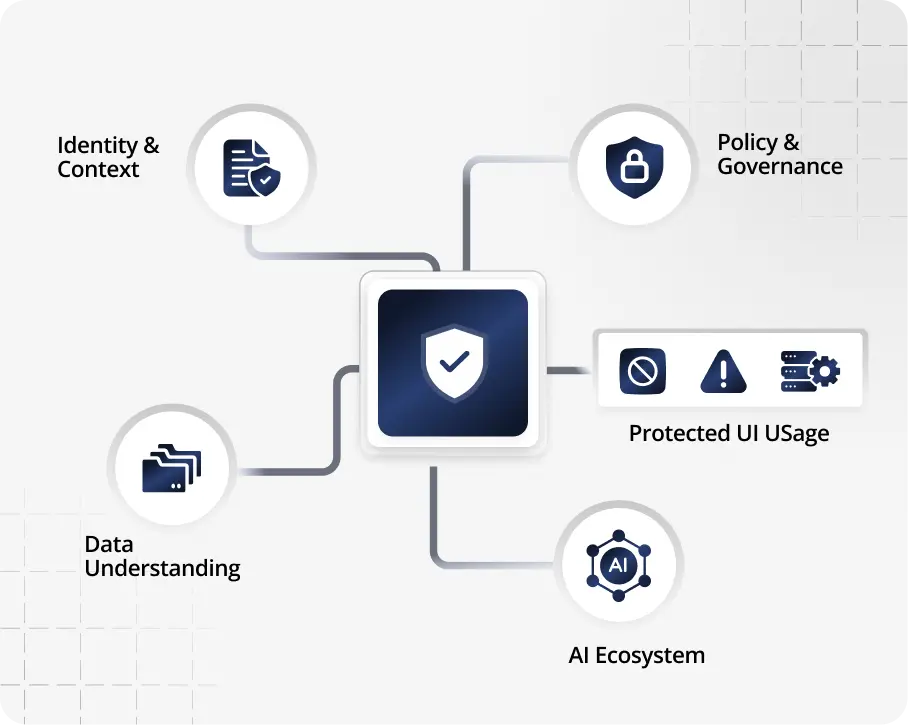
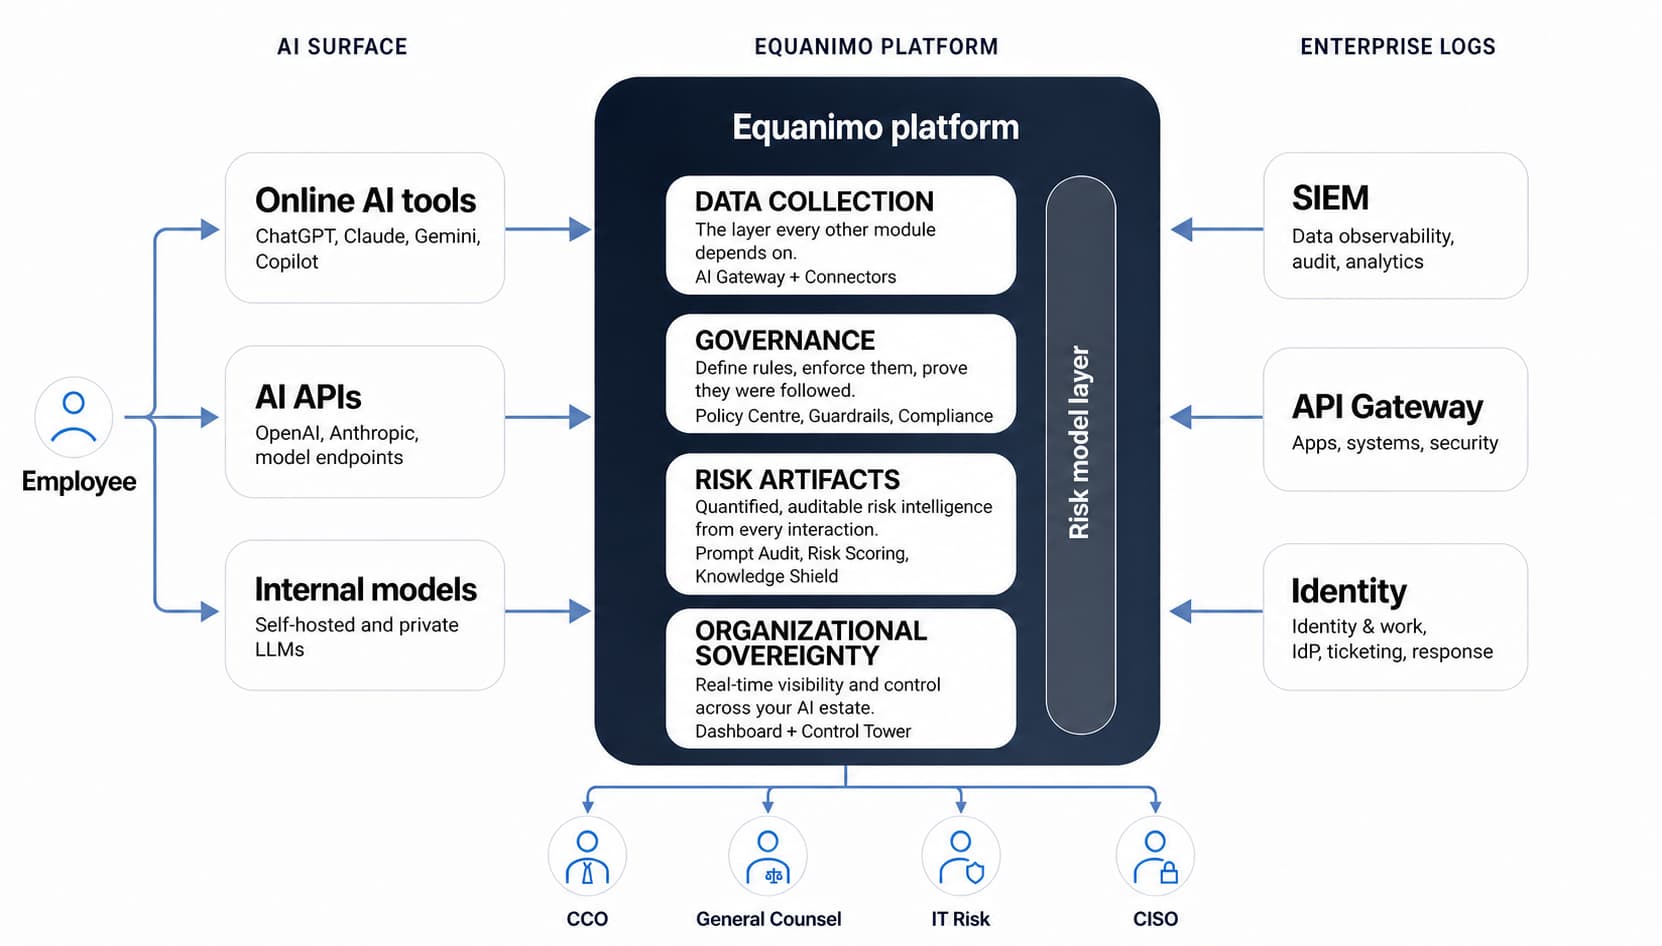
It evaluates user identity, personas, data sensitivity, business context, and organizational policies in real time to prevent unauthorized knowledge exposure. Built on a plug-and-play architecture, Equanimo integrates seamlessly with existing AI applications, APIs, and models without requiring application changes.
- Platform Overview
The Full Platform, At a Glance
Four module groups. One integrated platform.
— Command
Layer 4
Organizational Sovereignty
Real-time visibility and control across your AI estate.
Layer 3
— Evidence
Risk Artifacts
Quantified, auditable risk intelligence from every interaction.
Layer 2
— Policy
Governance
Define rules, enforce them, prove they were followed.
Layer 1
— Foundation
Data Collection
The layer every other module depends on.
- Layer 04 Command
Organizational Sovereignty
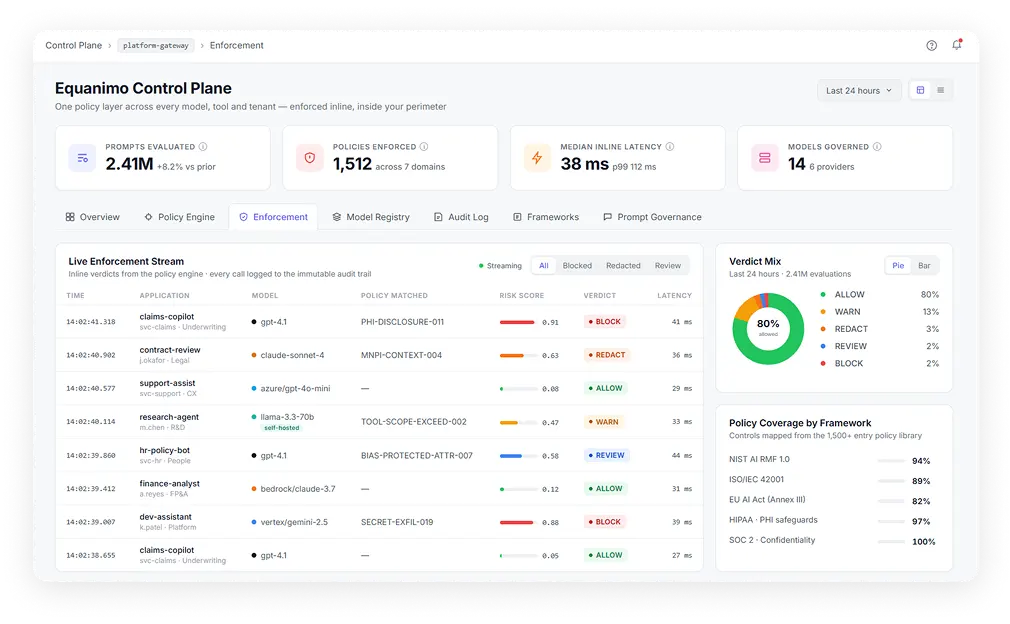
One view answers the question every CISO starts their day with: are we safe right now? Real-time visibility and instant action across your entire AI estate.
01
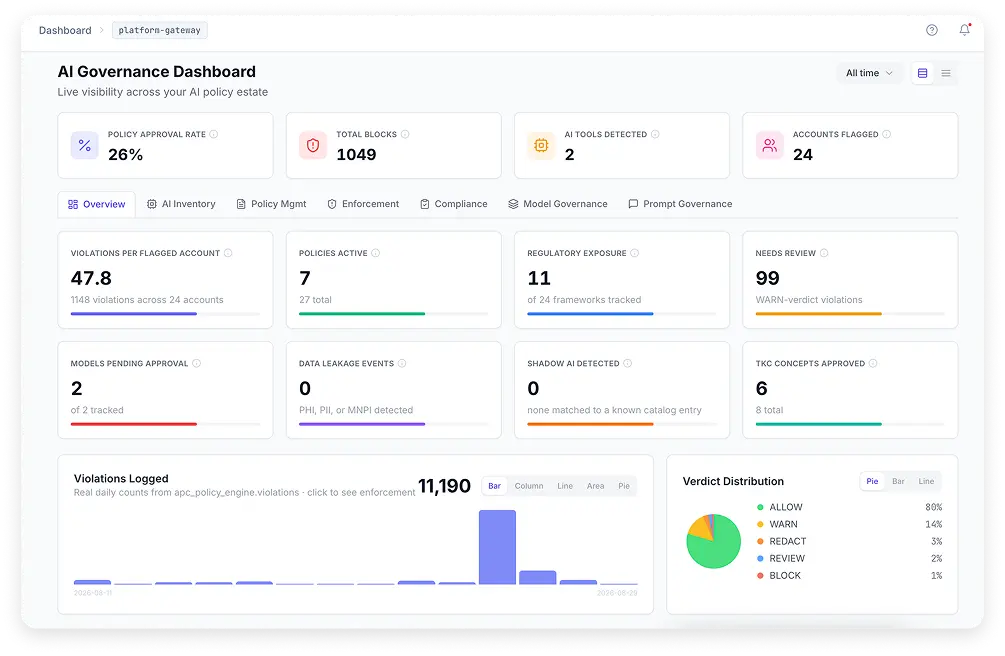
Dashboard
Compliance scores, risk flags, AI adoption and model activity — consolidated across every team into a single real-time view.
- Composite compliance score across GDPR, HIPAA, SOC 2, ISO 42001 and EU AI Act — with 7d / 30d / 90d trend
- AI adoption heatmap: approved vs shadow AI by team, live from Gateway traffic
- Top policy violations ranked by 24h trigger count with team attribution
- Cost & usage: prompts inspected, tokens processed, estimated AI spend
02
Control Tower
Every AI interaction as it happens — with the power to act immediately: suspend access, invoke a policy, or escalate an incident.
- Live prompt stream: every request transiting the Gateway in real time
- Inline policy execution — block, warn, quarantine or redirect without leaving the feed
- One-click user or team suspension, effective immediately at the Gateway layer
- Incident escalation with reviewer assignment, SLA tracking, and full audit trail
- LAYER 4 / COMMAND
FinOps & Cost Attribution
Spend Attribution
Track AI costs across business units, projects, models, and vendors so every dollar can be attributed to the right owner and use case.
Budget Controls
Compare actual spend against budgets, monitor consumption in real time, and identify potential overruns before they become costly.
ROI by Use Case
Measure the return generated by individual AI initiatives and identify which use cases are producing the strongest business impact.
Vendor Optimization
Identify duplicated services, idle usage, unnecessary model consumption, and inefficient vendor allocation.
- Layer 03 Evidence
Risk Artifacts
Quantified, auditable risk intelligence built from every AI interaction — detecting exposures in content, not just metadata.
01
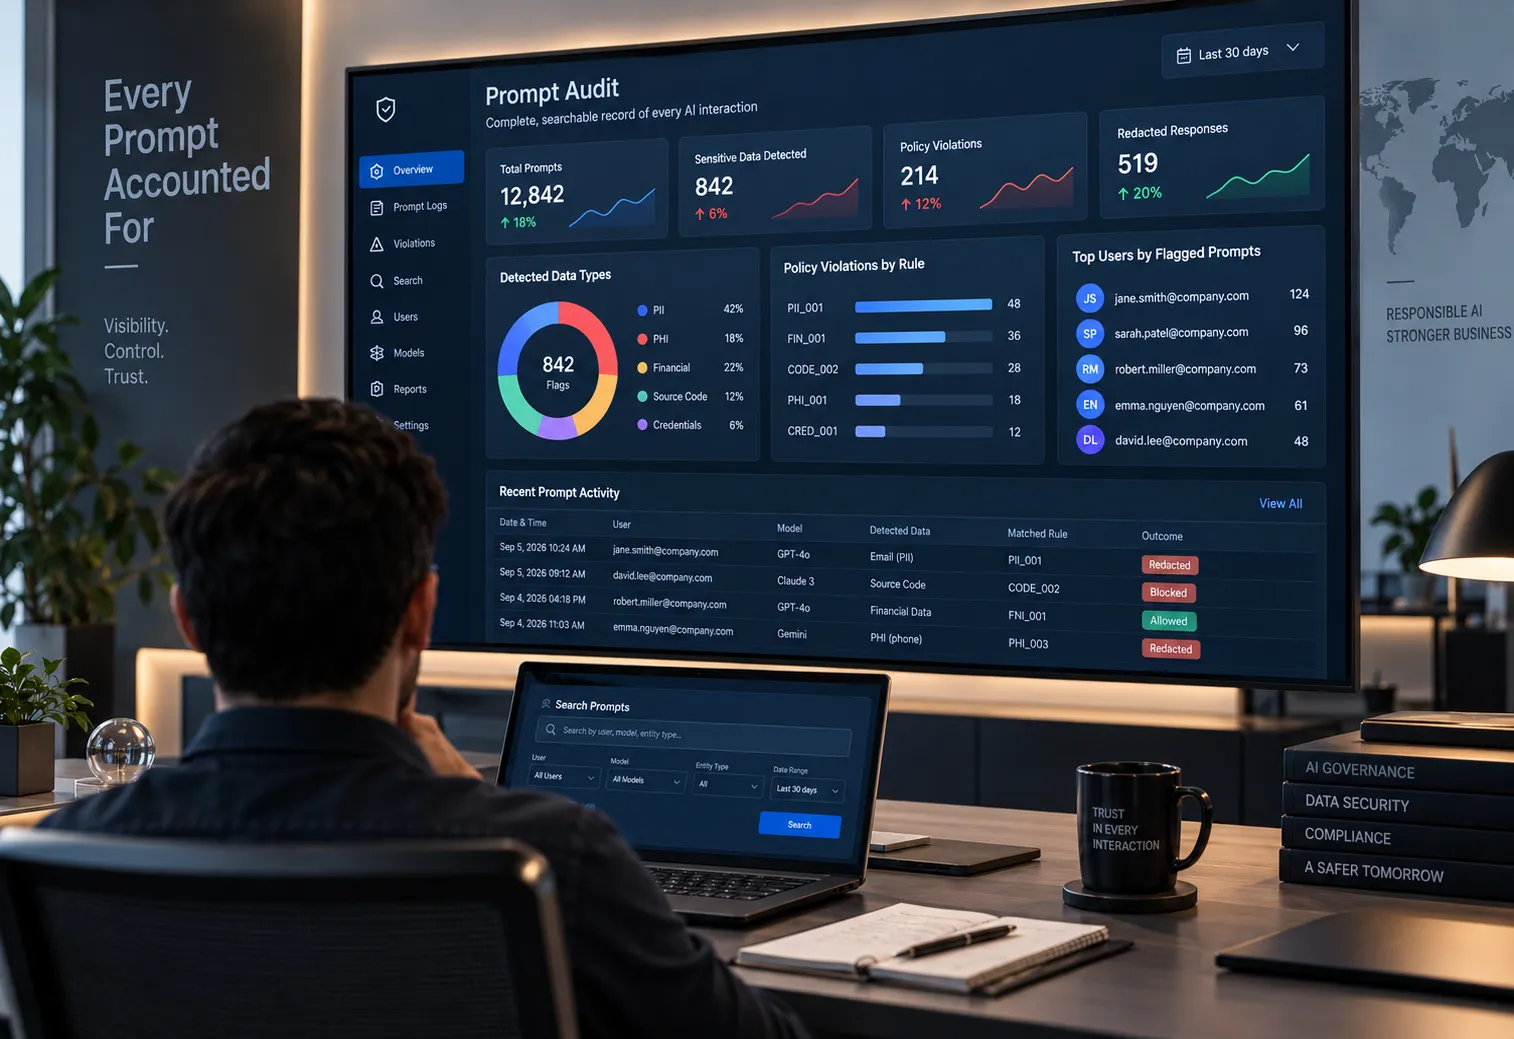
Prompt Audit
Complete, searchable record of every AI interaction — content-level detection of sensitive data, not just metadata.
- Full prompt log with PII, PHI, financial and source-code detection before storage
- Policy violation log with matched rule, triggering fragment and outcome
- Searchable by user, team, model, entity type and date
- Role-gated raw prompt access — with access itself written to the audit trail
02
Risk Scoring
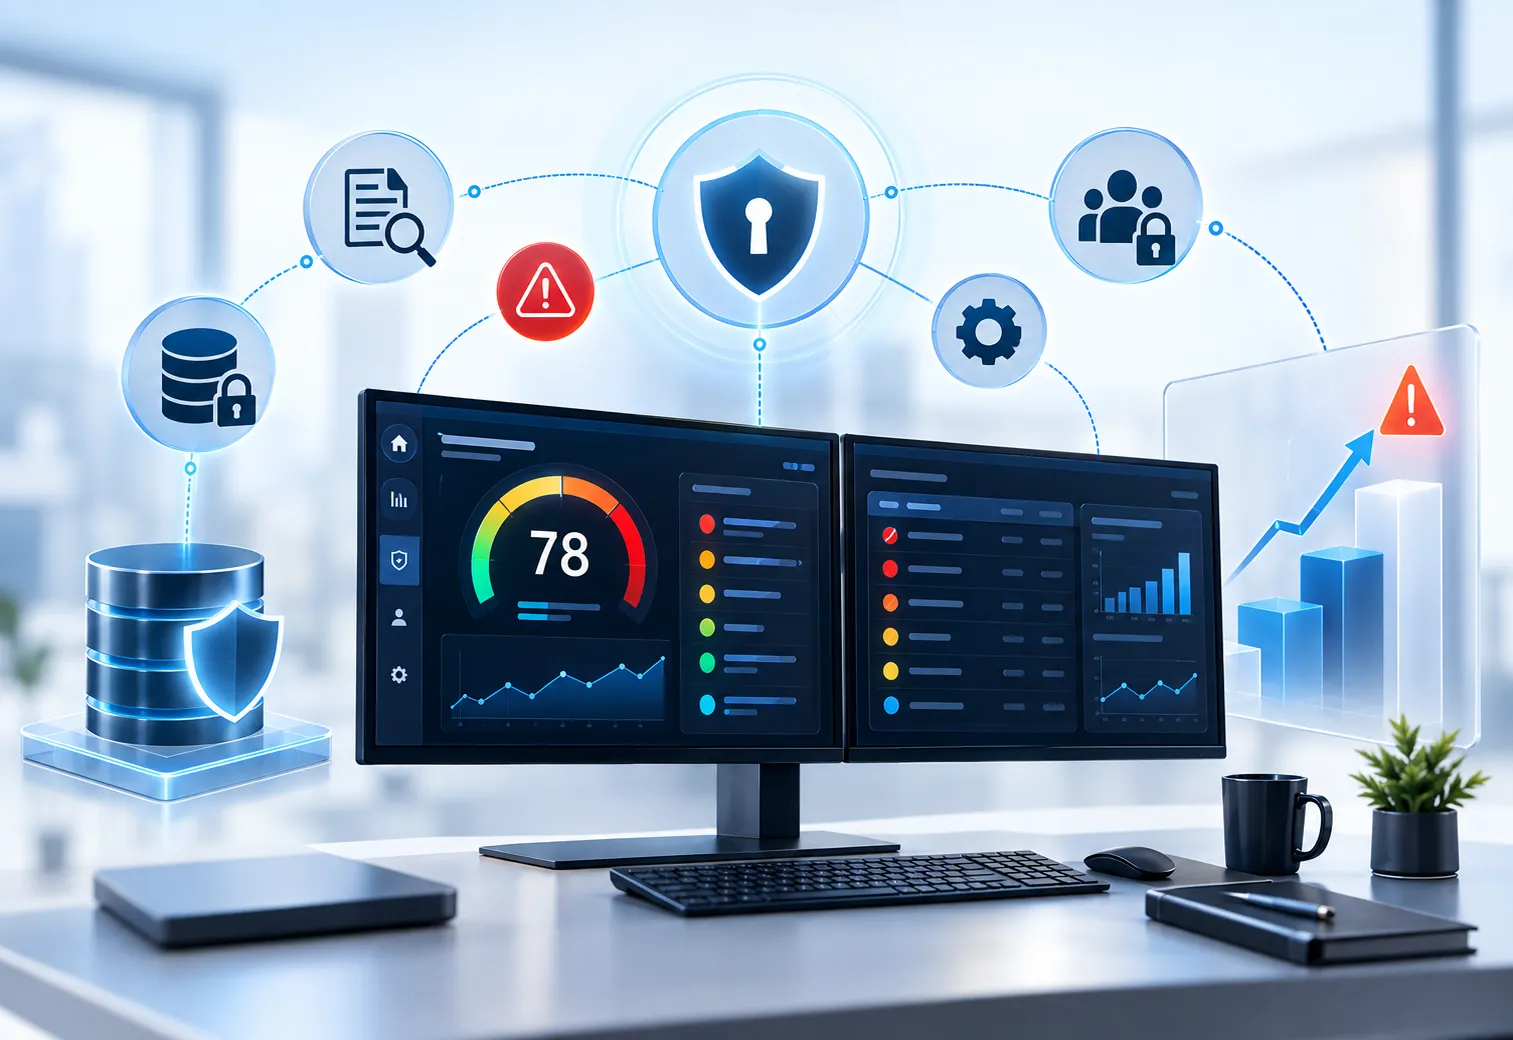
Continuous, evidence-based risk scores for every model, team and use case a live signal that drives remediation.
- Multi-factor composite score (0–100) with automatic escalation at Critical tier
- Remediation priority queue with suggested actions and drill-through
- Score history — prove governance actions are reducing exposure
03
Knowledge Shield
Real-time detection and blocking of proprietary information — source code, pricing models, client data — in prompts and responses.
- Knowledge fingerprinting — custom sensitive categories detected without exposing the content
- Bidirectional detection on outbound prompts and inbound AI responses
- Vector DB analysis — scheduled and on-demand scans of knowledge bases
- Layer 02 Policy
The Governance Layer
Define the rules that govern AI use, enforce them automatically, and generate the evidence that proves they were followed — continuously, not just at audit time.
01
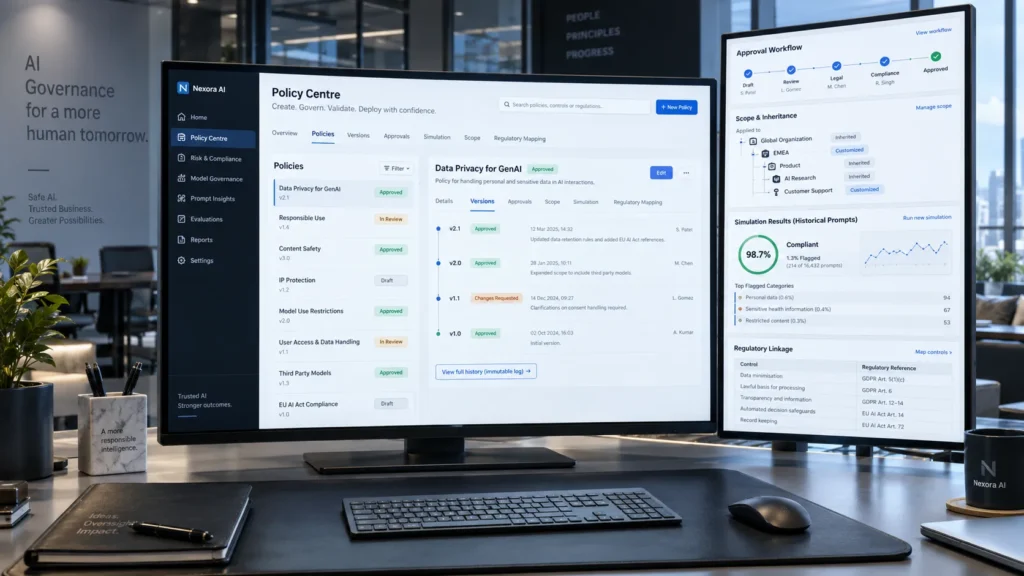
Policy Center
Author, version and publish AI governance rules as machine-readable controls — active at the Gateway the moment they’re approved.
- Structured authoring with full version control, approval workflows and immutable change history
- Scope targeting at org, BU, team or model level with inheritance rules
- Simulate a policy against historical prompt data before it goes live
- Controls linked to the regulatory articles they satisfy
02
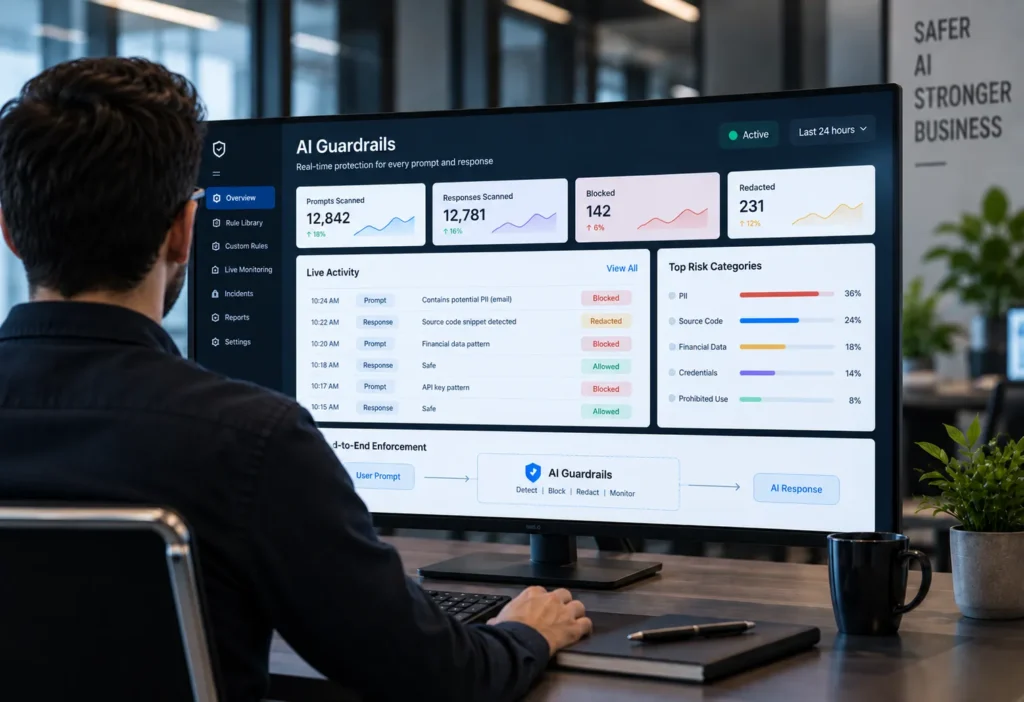
AI Guardrails
Real-time enforcement on every prompt and response — blocking, redacting or flagging before data moves.
- Pre-built library covering PII, source-code leakage, financial data, credentials and prohibited use
- Custom rule builder with pattern matching and ML classifiers
- Bidirectional enforcement on both inbound prompts and outbound responses
- Per-rule action: hard block, silent redaction, warn-and-allow or log-only
03
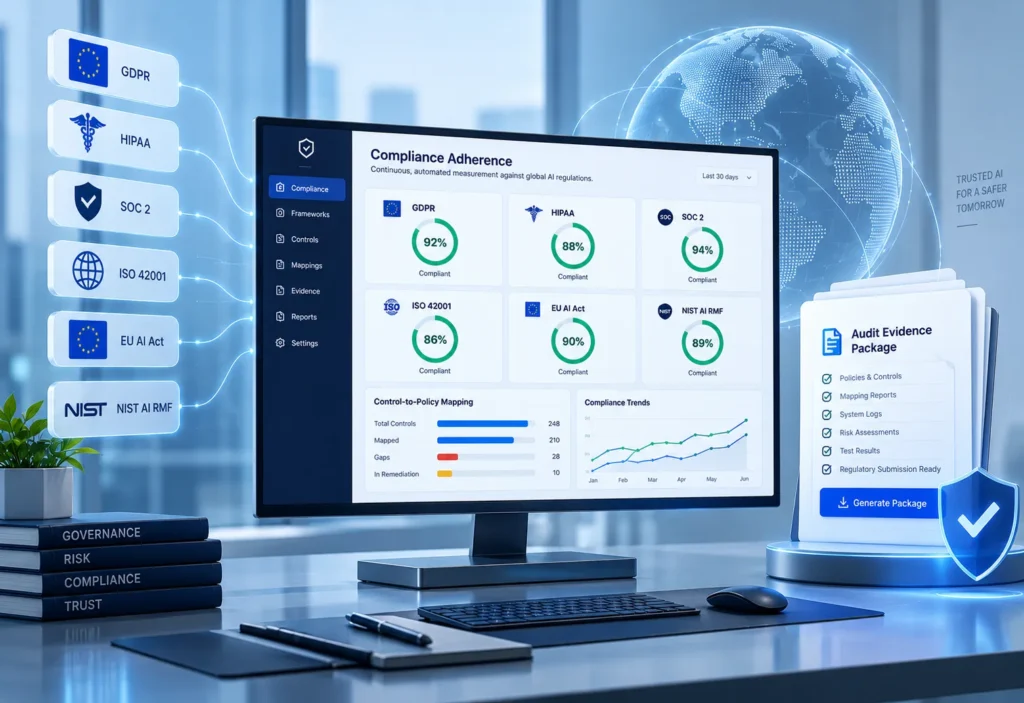
Compliance Adherence
Continuous, automated measurement against six regulatory frameworks — with one-click evidence packages ready for auditors.
- Live coverage dashboard for GDPR, HIPAA, SOC 2, ISO 42001, EU AI Act and NIST AI RMF
- Control-to-policy mapping with gap identification and remediation guidance
- One-click audit evidence package — formatted for regulatory submission
04
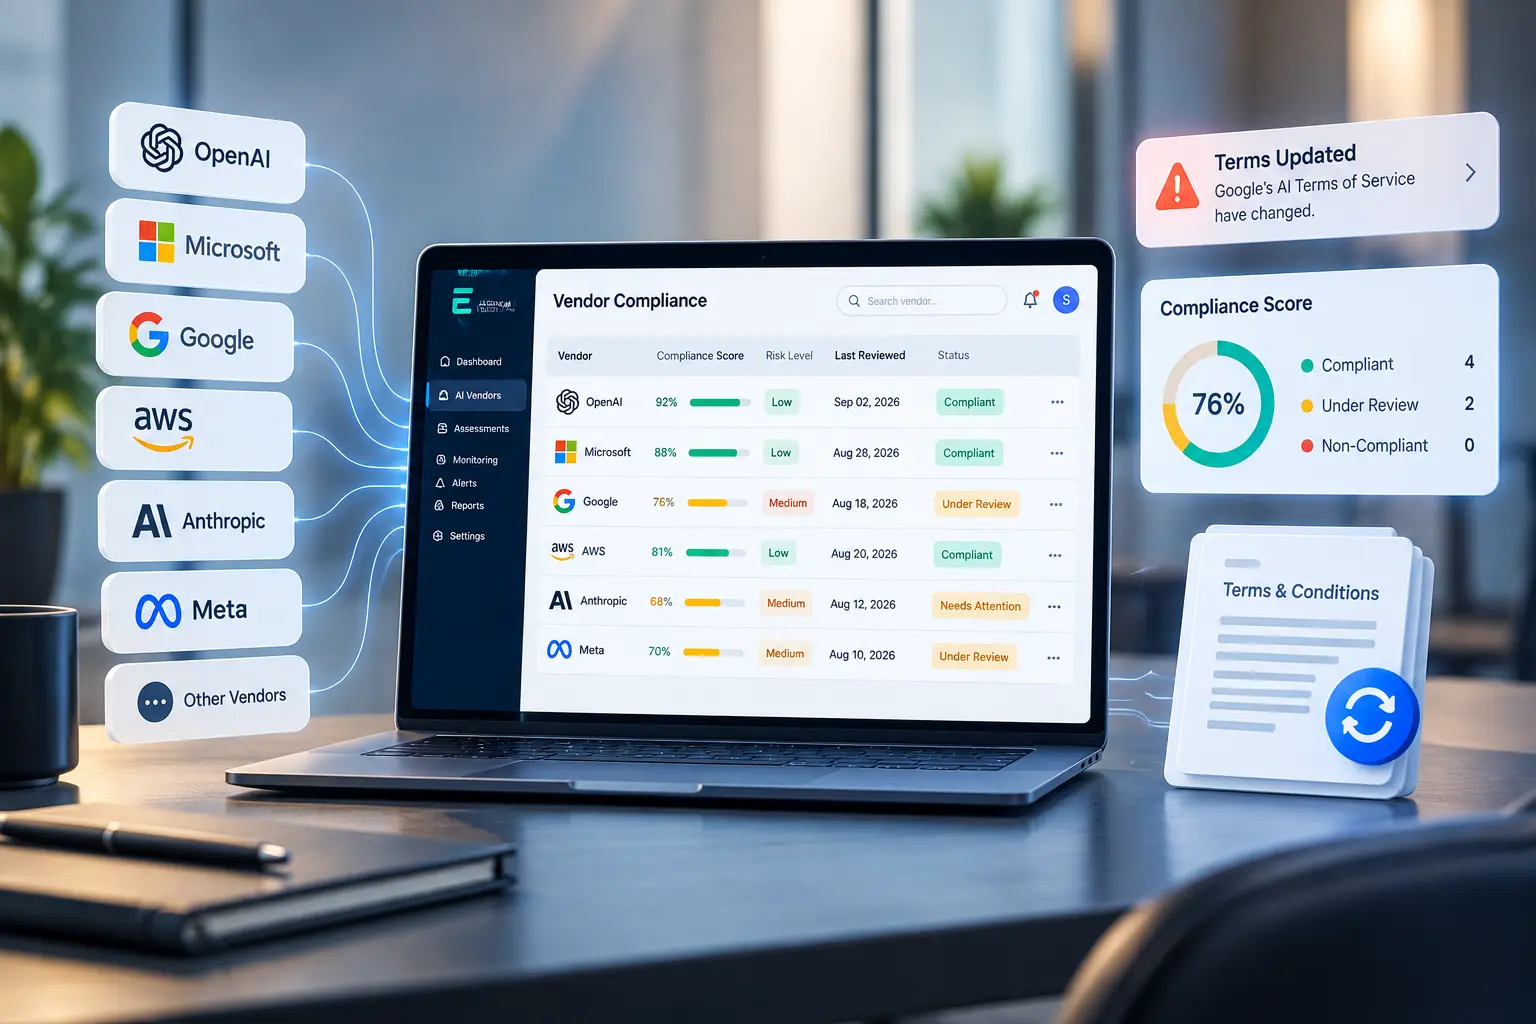
Vendor Compliance
Governance of every external AI vendor — scored against your framework, with automatic alerts when their terms change.
- Vendor registry auto-populated from Gateway traffic, with compliance scorecards per vendor
- DPA and contract tracker with permitted data categories, residency and expiry monitoring
- Alerts when terms, privacy policy or certifications change
- M2M INTERACTION GOVERNANCE
When AI Calls AI, Governance Follows
Your App → Approved LLM

- Layer 01 Foundation
Data Collection
Gateway intercepts and governs AI traffic at the network. Connectors extend that visibility to tools outside the network boundary. The layer everything else depends on.
01
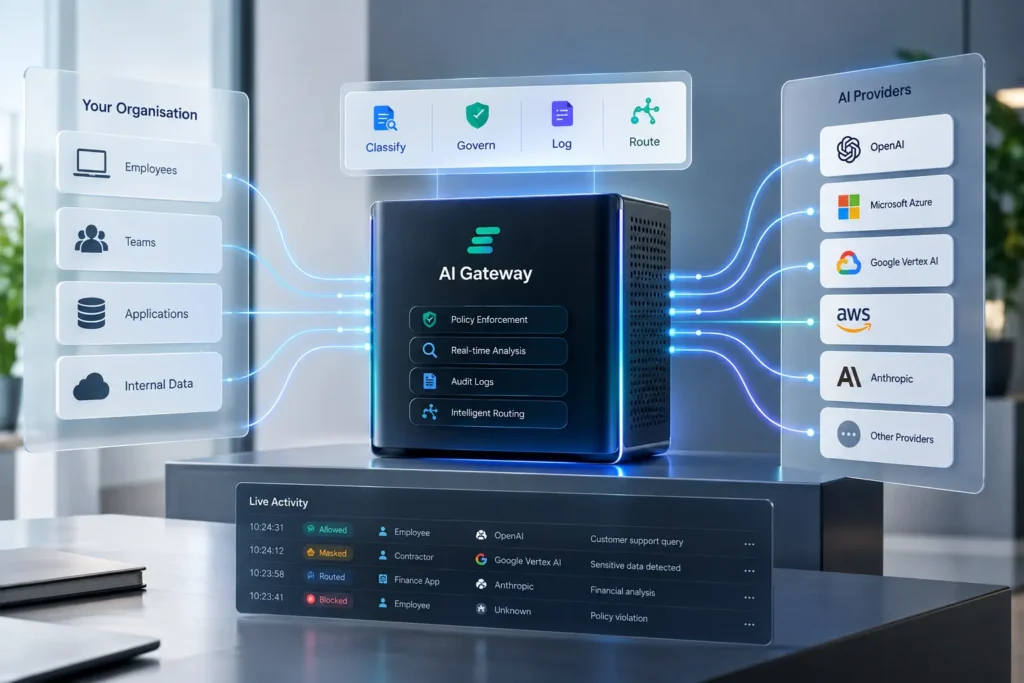
AI Gateway
A policy-enforced proxy between your organisation and every AI provider — every API call classified, governed, logged, and routed in real time.
- Unified proxy for OpenAI, Anthropic, Azure OpenAI, Gemini, Bedrock and internal models — no SDK changes required
- Authentication via your existing IdP over OIDC / SAML
- Real-time governance pipeline: classification, PII detection and guardrail evaluation at every request
- Rate limits, spend quotas, model routing, failover and data-residency region lock
02
Connectors
- Pre-built connectors for Microsoft Copilot for M365, GitHub Copilot and Salesforce Einstein
- SIEM integration with Splunk, Microsoft Sentinel and Datadog
- Identity provider sync — keep user rosters and roles consistent across the platform
- Platform Architecture
How Equanimo fits in.
Equanimo protects enterprise knowledge by understanding the full context behind every AI interaction—not just prompts, policies, or keywords. Built on a plug-and-play architecture, it integrates with existing AI applications, APIs, and models without requiring application changes.
- BUILT DIFFERENT
How Equanimo Compares
See how Equanimo extends beyond traditional security and AI governance tools with knowledge-level detection, M2M visibility, flexible capture, and native cost attribution.
| Feature | AI Security Platforms | DLP / SASE |
Equanimo
|
|---|---|---|---|
|
String-Matching Detection
|
Supported | Supported | Supported |
|
Semantic Knowledge Fingerprinting
|
— | — | Full |
|
M2M Interaction Tracking
|
Partial | — | Every Hop |
|
Network-Level Capture (I3)
|
— | Supported | Zero-Code I3 |
|
Native FinOps / Cost Attribution
|
Partial | — | Native |
- Get Started
See every module in a working environment.
A 45-minute demo against your own risk profile — focused on the modules most relevant to your compliance posture.